Field manual I · Applied Cryptography & P2P Mesh
Noctis
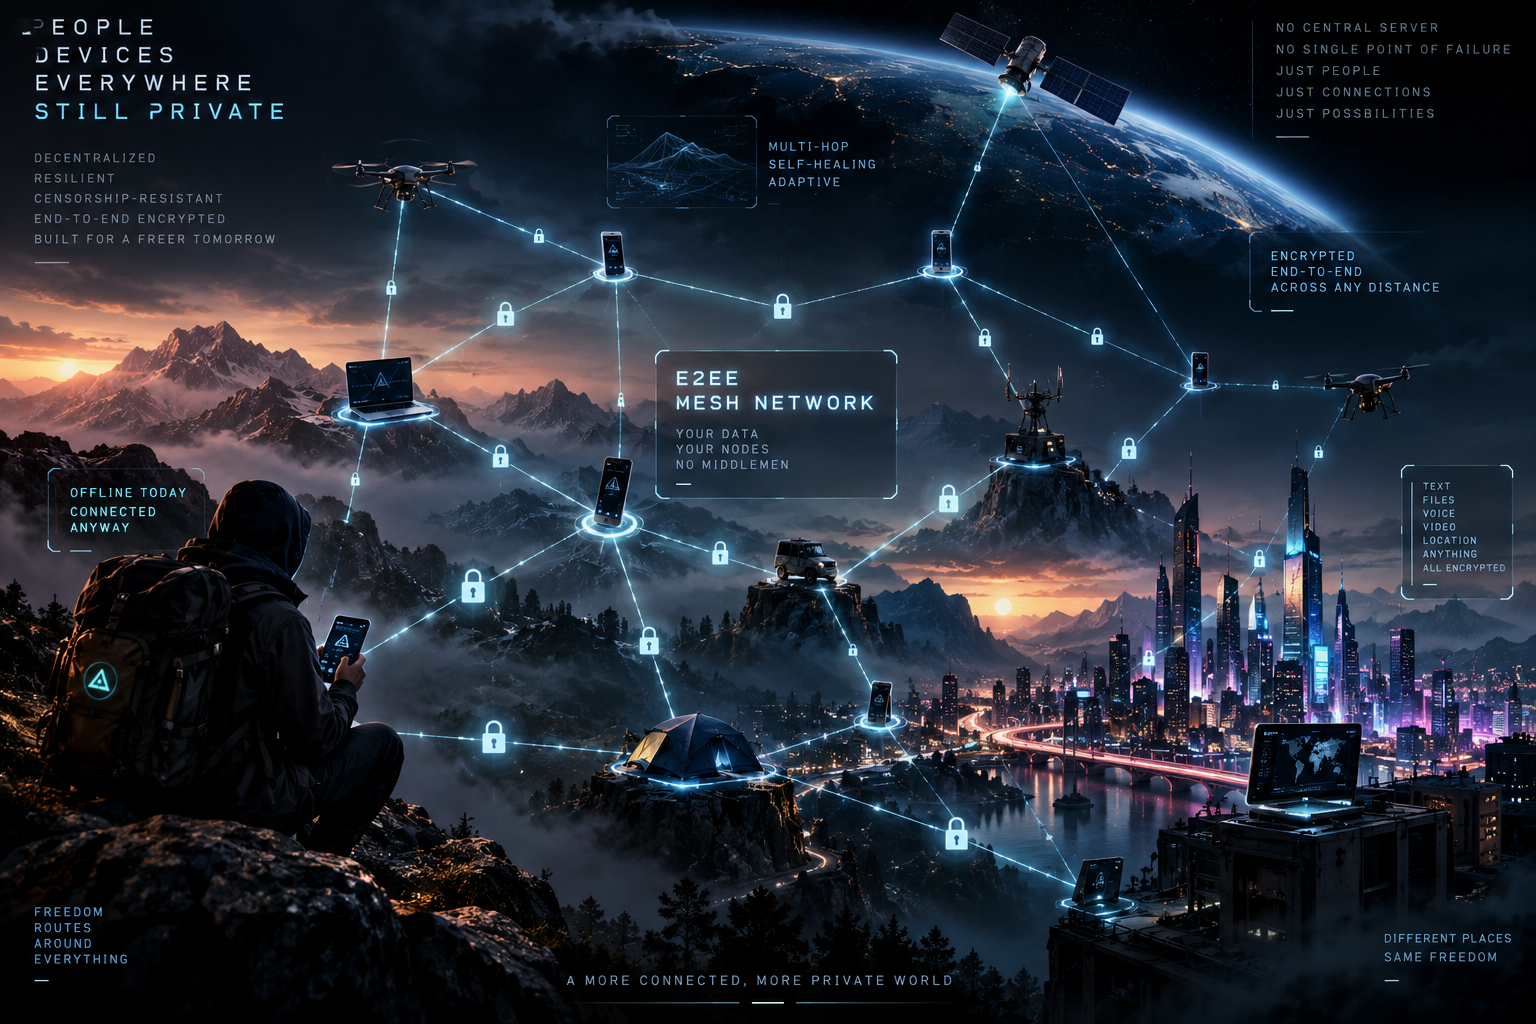
A zero-trust, end-to-end encrypted messaging engine operating across decentralized, multi-hop mesh topologies with zero intermediate plaintext exposure.

Chapter I
The perimeter bottleneck
Trustless multi-hop relays.
Decentralized mesh networks eliminate central choke points, but they force every intermediate node to act as an untrusted router. Traditional transport-layer encryption breaks at each hop boundary, forcing nodes to inspect payloads to route them.
Noctis decouples wire routing metadata from application payloads. Intermediate relays can forward packets across bounded TCP connections without accessing ephemeral keys or viewing plaintext data.
- Poly1305 AEAD
- ChaCha20
- Session agreement
- X25519
Chapter II
Cryptographic matrix
The security core.
Ed25519 identity
Each node generates an immutable Ed25519 signing keypair serving as its network identifier. Identity verification happens at session handshake time, preventing spoofing and impersonation.
HKDF-SHA-256
Derives separate symmetric keys for transmission and reception from ephemeral Diffie-Hellman secrets. Every session operates within isolated cryptographic bounds with ratchet-ready properties.
Bounded relays
Enforces sequence-based sliding windows to drop replayed packets, uses bounded TCP buffer rings, and decrements strict TTL values to kill forwarding loops across untrusted peers.
Chapter III
The outcome
Verified protocol integrity.
Test suite passing


Chapter IV
Apparatus
Concurrent, memory-safe Go architecture paired with verified cryptographic primitives.
- Go 1.21Core engine
- x/cryptoAEAD & curves
- ProtobufWire format
- Fyne v2GUI